Device Identity
- Manufacturer
- Model
- Serial number
- Capacity
- Interface
- Firmware
CertifiedNIST SP 800-88 Rev. 2 · DoD 5220.22-M · IEEE 2883
NSA/CSS Storage Device Sanitization
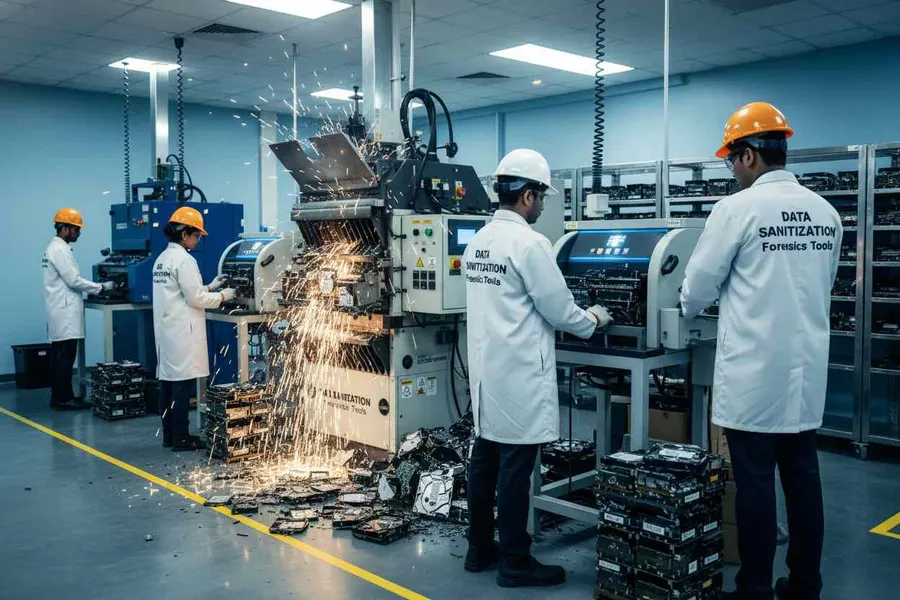
NSA/CSS Policy Manual 9-12 is the NSA/CSS Storage Device Sanitization Manual, providing guidance for the sanitization of information-system storage devices for disposal or recycling.
The current publicly released manual is dated 19 February 2026 and applies to NSA/CSS elements, contractors and personnel. It addresses storage devices containing information ranging from unclassified material through highly sensitive and classified information and provides information concerning NSA/CSS-evaluated sanitization equipment.
For organizations that require an NSA/CSS Policy Manual 9-12-based sanitization workflow, Data Sanitization Pro (DSP) provides a dedicated NSA/CSS Policy Manual 9-12 Sanitization Method through the DSP Sanitization Engine, with device assessment, controlled execution, verification and audit-ready documentation.
Important: NSA/CSS Policy Manual 9-12 should not be represented as an ordinary fixed-pass disk-wiping algorithm. It is a storage-device sanitization and destruction policy/manual whose applicable procedure depends on the storage technology, information sensitivity, disposition requirements and approved sanitization or destruction equipment.
NSA/CSS Policy Manual 9-12 provides guidance for the secure disposition of information-system storage devices.
The manual is associated with:
The NSA's Center for Storage Device Sanitization Research (CSDSR) maintains guidance and evaluated-product information for storage-device sanitization and destruction.
Unlike historical wiping methodologies that are commonly described by a fixed number of software overwrite passes, NSA/CSS Policy Manual 9-12 is broader than a single overwrite sequence.
The policy framework covers information-system storage devices used by NSA/CSS elements, contractors and personnel.
The publicly released policy documentation identifies storage formats including:
The associated policy statement describes processes for the sanitization and release of information-system storage devices, while the manual provides the detailed sanitization and disposition guidance.
This technology-specific approach is important because the correct sanitization technique depends on how information is physically and logically stored.
A common misconception is to treat NSA/CSS 9-12 as another fixed multi-pass overwrite method such as Gutmann, Schneier, HMG IS5 or historical DoD overwrite profiles.
That is not the correct technical framing.
NSA/CSS Policy Manual 9-12 provides a broader framework around storage-device sanitization and destruction.
The appropriate process can depend on:
The NSA's current public guidance also maintains Evaluated Product Lists for equipment meeting NSA specifications, including categories such as HDD destruction devices, magnetic degaussers and solid-state disintegrators.
DSP provides a dedicated NSA/CSS Policy Manual 9-12 Sanitization Method within the DSP Sanitization Engine.
IDENTIFY Identify the target storage device.
CLASSIFY Determine storage technology and relevant device characteristics.
ASSESS Assess device accessibility, health, errors and applicable sanitization conditions.
SELECT Select the NSA/CSS Policy Manual 9-12 method.
EXECUTE Execute the applicable DSP sanitization operation.
VERIFY Verify the recorded sanitization result.
VALIDATE Determine whether the result satisfies the applicable organizational requirement.
DOCUMENT Record device, method, operator, system and verification information.
CERTIFY Generate an audit-ready sanitization certificate documenting the operation performed.
NSA/CSS 9-12 is particularly relevant because storage technologies do not all behave the same way.
Traditional magnetic hard disk drives can support sanitization techniques based on their magnetic storage architecture and applicable organizational requirements.
DSP can record:
Modern SSD and NVMe devices use controller-managed flash architectures.
Relevant characteristics can include:
Consequently, a conventional host-level overwrite should not automatically be presented as equivalent to complete physical sanitization of an SSD or NVMe device.
The applicable device-specific sanitization capability and organizational security requirement should be assessed before execution.
NSA/CSS 9-12 also covers storage technologies beyond conventional HDDs. The NSA maintains evaluated equipment categories for multiple media types, including optical destruction and solid-state disintegration.
One of the most important characteristics of the NSA/CSS approach is the distinction between sanitization and physical destruction.
Sanitization attempts to render stored information inaccessible according to the applicable security requirement while potentially allowing the media to remain usable.
Destruction physically compromises the storage medium so that recovery of the information is prevented according to the applicable destruction requirement.
For certain high-security or technically unsuitable storage devices, destruction may be the required disposition rather than conventional software wiping.
The current NSA Evaluated Products Lists include dedicated categories for:
NSA/CSS maintains Evaluated Products Lists (EPLs) identifying equipment that meets applicable NSA specifications.
The NSA explains that these lists apply to NSA/CSS elements, contractors and personnel and are used in connection with Policy Manual 9-12 disposal or recycling activities.
This creates an important distinction for DSP:
DSP software support for an NSA/CSS 9-12 workflow does not mean DSP itself is an NSA-evaluated sanitization device or that DSP software is automatically listed on an NSA EPL.
The website should never use phrases such as:
unless a separate official evaluation exists.
Professional sanitization begins with understanding the device being processed.
DSP can collect and document information such as:
This information helps establish an auditable relationship between the physical storage device and the sanitization operation.
A damaged storage device introduces an important sanitization question:
DSP can identify and report:
If the required sanitization operation cannot be reliably completed, the result should be evaluated against the organization's applicable security and disposition policy.
This is especially important for:
DSP separates verification from validation.
Verification determines whether the selected sanitization operation completed as recorded.
DSP can document:
Validation determines whether the resulting condition satisfies the applicable organizational sanitization requirement.
This distinction is particularly important for high-security environments.
A completed software process does not automatically establish that the organization's required security outcome has been achieved in every storage architecture.
The NSA/CSS policy documentation specifically addresses storage devices containing information ranging from UNCLASSIFIED to TOP SECRET, including compartmented, sensitive and limited-distribution information.
This makes the policy fundamentally different from consumer-oriented “delete” or “format” functionality.
A professional sanitization workflow must consider:
NSA/CSS Policy Manual 9-12 specifically provides guidance for sanitization of storage devices intended for disposal or recycling.
This makes the methodology relevant to controlled asset-disposition environments where organizations need documented evidence that storage devices were processed before leaving their controlled environment.
Potential applications include:
DSP can generate an audit-ready sanitization certificate documenting the operation performed by the DSP Sanitization Engine.
The certificate can include:
The certificate documents the operation performed by DSP. It is not an NSA-issued certificate, NSA/CSS approval, NSA EPL listing or certification from the U.S. Government.
| Characteristic | NSA/CSS Policy Manual 9-12 | Historical Multi-Pass Methods |
|---|---|---|
| Primary Concept | Storage-device sanitization & destruction | Defined overwrite sequence |
| Fixed Pass Count | Not the defining characteristic | Often yes |
| Media-Specific Approach | ✓ Yes | Often limited |
| Physical Destruction | Included in overall disposition framework | Usually separate |
| Evaluated Equipment | NSA EPL framework | Generally not applicable |
| HDD | Applicable | Common target |
| SSD/NVMe | Technology-specific consideration | Conventional overwrite limitations |
| Classified/sensitive Information | Explicitly addressed | Varies |
| Audit Documentation | Important | Depends on implementation |
| Current NSA/CSS Framework | ✓ Yes | Usually historical methodology |
Both frameworks emphasize that storage sanitization must be considered in relation to the storage technology and security requirement, but they originate from different organizations and serve different policy environments.
| Area | NSA/CSS Policy Manual 9-12 | NIST SP 800-88 Rev. 2 |
|---|---|---|
| Organization | NSA/CSS | NIST |
| Primary Focus | NSA/CSS storage-device sanitization & destruction | Media sanitization program/guidance |
| Environment | NSA/CSS and associated personnel/contractors | Broad organizational use |
| Storage Technology | Media-specific | Media-specific |
| Physical Destruction | Covered | Covered as a sanitization category |
| Device-Specific Methods | Important | Important |
| Evaluated Equipment | NSA EPL framework | NIST does not create an equivalent NSA EPL |
| Fixed Multi-Pass Algorithm | Not the defining model | Not the defining model |
NIST SP 800-88 Rev. 2 is a separate current media-sanitization publication and should not be represented as identical to NSA/CSS Policy Manual 9-12.
Sensitive environments may require sanitization without Internet connectivity.
DSP supports controlled offline operation for environments such as:
Device processing and sanitization records can be generated locally without requiring the target device to be connected to the public Internet.
Enterprise and ITAD operations may involve multiple storage devices.
DSP can maintain device-specific records so that each processed device has its own:
This allows organizations to maintain individual device traceability rather than relying on a single batch-level record.
DSP provides a dedicated workflow for organizations that need to document an NSA/CSS Policy Manual 9-12-based sanitization process.
DSP should be positioned accurately:
NSA/CSS Policy Manual 9-12 is an NSA/CSS storage-device sanitization and destruction manual.
DSP provides a dedicated software sanitization method and documents the operation executed by its Sanitization Engine.
DSP certification documents the actual operation performed by DSP.
It does not mean:
unless such authorization or evaluation is separately established.
Modern storage sanitization cannot be reduced to a simple “number of passes.”
A professional workflow considers:
WHAT DATA? WHERE IS IT STORED? WHAT STORAGE TECHNOLOGY IS USED? CAN THE REQUIRED AREAS BE ADDRESSED? WHICH SANITIZATION OR DESTRUCTION TECHNIQUE APPLIES? CAN THE RESULT BE VERIFIED? DOES THE RESULT SATISFY THE ORGANIZATION'S SECURITY REQUIREMENT?
This technology-aware approach is central to professional storage-device sanitization.
NSA/CSS Policy Manual 9-12 provides a structured framework for secure storage-device sanitization and destruction within the NSA/CSS environment.
DSP brings that policy reference into a modern software workflow with:
The result is a controlled, traceable and documented sanitization operation.
NSA/CSS Policy Manual 9-12 Storage Device Sanitization Executed through the DSP Sanitization Engine Verified and Documented with an Audit-Ready Sanitization Certificate
It is the NSA/CSS **Storage Device Sanitization Manual**, providing guidance for sanitizing storage devices for disposal or recycling and describing applicable sanitization/destruction procedures and evaluated equipment.
No. It should not be presented as a universal fixed seven-pass overwrite algorithm. It is a broader storage-device sanitization and destruction framework.
Yes. The NSA publicly released a version dated **19 February 2026**.
The policy framework covers storage devices including solid-state media. The appropriate sanitization or destruction approach depends on the specific storage technology and applicable requirements.
No. DSP can generate an **audit-ready certificate documenting the operation performed by DSP**. That certificate is not an NSA/CSS-issued certification.
NSA Evaluated Product Lists identify equipment that meets applicable NSA specifications. Current NSA lists include categories such as HDD destruction devices, magnetic degaussers, optical destruction devices and solid-state disintegrators.
The policy manual specifically addresses storage-device sanitization for disposal or recycling. Organizations using it should apply the requirements appropriate to their environment, information sensitivity and storage technology.
No. They are separate publications from different U.S. organizations. NSA/CSS 9-12 is an NSA/CSS storage-device sanitization and destruction manual, while NIST SP 800-88 is NIST's media-sanitization guidance.
Data Sanitization Pro runs all 25 standards offline and verifies the result.