What Does Compliance Mean When Data Leaves Your Control?
When a laptop, hard drive, SSD, server or other data-bearing device reaches the end of its useful life, deleting files is not the same as securely disposing of the data.
Organizations need a controlled process for deciding:
- When data should be removed
- Which storage media require sanitization
- How the media will be sanitized or destroyed
- How the result will be verified
- What records should be retained
- Who is responsible for the asset
- What happens before the device is reused, transferred, sold or recycled
Different laws, regulations and industry frameworks address these obligations differently.
No single data erasure method makes an organization automatically compliant.
Instead, secure data erasure software can form one part of a broader data retention, disposal, security and asset-management program.
Data Erasure Compliance: The Five Frameworks
The most useful way to understand compliance is to separate the requirement from the technical implementation.
| Framework | Main Focus | Relevance to Data-Bearing Media | What Organizations Should Document |
|---|---|---|---|
| DPDP Act 2023 | Personal data protection in India | Appropriate handling and erasure of personal data where applicable | Asset, process, responsibility and applicable erasure records |
| GDPR | Personal data protection | Storage limitation, erasure rights and appropriate security measures | What was erased, why, when and how the process was controlled |
| HIPAA | Protected health information | Secure disposal or reuse of electronic media containing ePHI | Media/device, disposal method and responsible process |
| PCI DSS | Payment/cardholder data security | Secure deletion or rendering cardholder data unrecoverable when no longer required | Disposal policy, media/process records and evidence |
| R2v3 | Responsible electronics reuse/recycling | Documented data sanitization before reuse or downstream transfer | Per-device sanitization records and chain-of-custody evidence |
These frameworks should not be treated as interchangeable. Each has its own scope, definitions, exceptions and organizational responsibilities.
DPDP Act 2023 & Data Erasure in India
For organizations operating in India, the Digital Personal Data Protection Act, 2023 is an important part of the privacy landscape.
The Act includes provisions concerning the erasure of personal data in specified circumstances, subject to applicable retention requirements and other legal obligations.
That means organizations should have a clear understanding of:
- What personal data they hold
- Why it is being retained
- When it should be erased
- Where copies may exist
- Who is responsible for the process
- How the disposal activity is documented
Data Erasure for Indian Organizations
For retired laptops, HDDs, SSDs, servers and other storage devices, secure media sanitization can help address the technical side of removing data from physical media.
A data erasure certificate can then provide an asset-level record of the operation.
Important: Data Sanitization Pro can support the technical erasure and documentation workflow; using the software alone does not make an organization DPDP compliant.
GDPR & Secure Data Erasure
The GDPR includes the principle of storage limitation, meaning personal data should generally not be retained in identifiable form longer than necessary for the purposes for which it is processed. Article 17 also establishes a right to erasure in specified circumstances, subject to exceptions.
For organizations handling EU personal data, this can make secure disposal an important part of the information lifecycle.
What Should Organizations Consider?
A practical data disposal program should consider:
- Data retention periods
- Approved disposal procedures
- Storage locations
- Physical devices
- Reuse and resale workflows
- Third-party processors
- ITAD providers
- Verification
- Documentation and accountability
GDPR compliance is broader than deleting a hard drive. However, properly controlled media sanitization can be an important technical control when personal data exists on physical storage.
HIPAA & Electronic Media Disposal
Healthcare organizations face additional considerations when electronic media contains protected health information (PHI).
The U.S. Department of Health and Human Services explains that HIPAA requires covered entities to have policies and procedures addressing the final disposition of ePHI and the hardware or electronic media on which it is stored. It also requires appropriate safeguards during disposal.
Appropriate approaches can include:
- Clearing
- Purging
- Physical destruction
depending on the circumstances and media involved.
HIPAA Data Erasure Documentation
For retired healthcare equipment organizations should be able to establish a controlled process for:
- Identify
- Sanitize
- Verify
- Document
- Dispose or Reuse
A detailed data erasure record can help connect the completed sanitization activity to the specific asset.
PCI DSS & Secure Deletion of Cardholder Data
PCI DSS addresses the protection and retention of payment card data.
PCI Security Standards Council guidance states that organizations should have a data retention and disposal policy and that once cardholder data is no longer required, it must be securely deleted or rendered unrecoverable.
This makes secure disposal relevant to systems and media that may contain:
- Cardholder data
- Payment system information
- Retired point-of-sale equipment
- Storage devices
- Backup media
- Other data-bearing hardware
PCI DSS Data Disposal
A controlled workflow should define:
- What data must be retained
- When it can be disposed of
- Which media contains it
- Which approved disposal method is used
- How the result is documented
Using data erasure software does not by itself make an organization PCI DSS compliant.
R2v3 & Data Sanitization for Electronics Reuse
R2v3 is particularly relevant to organizations involved in electronics reuse, refurbishment and recycling.
For these businesses, data-bearing equipment can move through multiple stages:
- Collection
- Testing
- Data Sanitization
- Refurbishment
- Resale
- Recycling
Data sanitization therefore needs to be integrated into the asset workflow rather than treated as an informal final step.
Why Per-Device Records Matter
A statement such as:
“All drives were wiped.”
does not provide the same level of traceability as records associated with individual assets.
A stronger workflow can connect:
- Asset
- Serial Number
- Sanitization Process
- Verification
- Final Disposition
This is particularly valuable for ITAD providers, refurbishers and electronics recyclers.
Compliance Does Not Mean “Use More Passes”
One of the biggest misconceptions about data erasure compliance is that regulations require a specific number of overwrite passes.
They generally do not work that way.
The appropriate technical approach depends on:
- The applicable requirement
- Data sensitivity
- Storage technology
- Device capabilities
- Final disposition
- Organizational policy
- Risk assessment
- Required assurance
Current NIST SP 800-88 Rev. 2 focuses on establishing an enterprise media sanitization program and selecting appropriate sanitization techniques and controls based on the sensitivity of information. It also references current approaches such as IEEE 2883 and cryptographic erase.
So the question should not simply be:
“How many passes does compliance require?”
It should be:
“What sanitization process is appropriate for this media, data and disposition?”
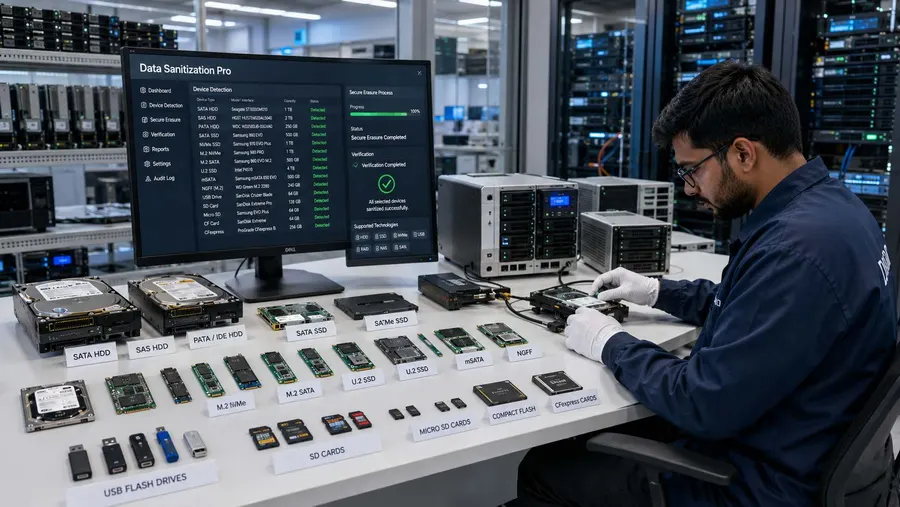
NIST SP 800-88 & Compliance
NIST SP 800-88 Rev. 2 is a major reference for media sanitization.
The current revision was published on September 26, 2025 and superseded Rev. 1.
NIST describes media sanitization as a process intended to make access to target data infeasible for a given level of effort. The current guidance focuses on establishing an organizational media sanitization program with appropriate techniques and controls.
For organizations building a secure asset retirement process, NIST can therefore help provide a framework for:
- Media identification
- Sanitization decisions
- Approved techniques
- Organizational controls
- Validation
- Disposal
- Reuse
- Documentation
What Should a Data Erasure Compliance Process Include?
A practical process should cover more than the erase operation itself.
- 01
Identify the Asset
Record the device and relevant asset information.
- 02
Determine the Data & Risk
Understand what type of information may be stored on the media and how sensitive it is.
- 03
Determine the Disposition
Will the device be:
- Reused?
- Redeployed?
- Resold?
- Returned?
- Recycled?
- Physically destroyed?
- 04
Select the Sanitization Method
Choose an appropriate method based on the storage technology, policy and applicable requirements.
- 05
Perform the Erasure
Run the approved sanitization operation.
- 06
Verify the Result
Check whether the intended sanitization was completed successfully.
- 07
Generate Evidence
Create the appropriate certificate or report.
- 08
Complete the Asset Disposition
Release, reuse, transfer, recycle or destroy the media according to the organization's approved process.
Data Erasure Certificate & Compliance Evidence
A data erasure certificate does not replace a compliance program.
It provides evidence about a particular asset and operation.
Useful information can include:
- Device model
- Serial number
- Capacity
- Firmware
- Selected sanitization method
- Standard
- Processing status
- Verification result
- Date and time
- Operator
- Organization
- Host system
- Other audit information
This helps create a connection between:
- POLICY
- ASSET
- ERASURE
- VERIFICATION
- RECORD
For more information about the documents generated by Data Sanitization Pro:
Data Erasure Compliance for ITAD & Recyclers
ITAD companies handle equipment that frequently changes ownership or moves through multiple processing stages.
That creates an important question:
Can the organization prove that the data was removed before the device moved to its next destination?
A controlled workflow can include:
- Receive
- Record
- Test
- Sanitize
- Verify
- Certificate
- Release
For larger operations, asset-level records can also support reconciliation between physical devices and their corresponding erasure documentation.
Data Erasure Compliance for Enterprises
Enterprise IT departments can build secure media disposal procedures around:
- Employee laptop retirement
- Desktop replacement
- Server decommissioning
- Data center equipment retirement
- Storage upgrades
- Lease returns
- Hardware resale
- IT asset disposal
- Recycling
The important part is consistency.
Every asset should follow the organization's approved process rather than relying on an employee manually deleting files or formatting a drive.
What Happens When a Drive Cannot Be Sanitized?
Not every storage device will successfully complete every sanitization operation.
A drive may:
- Fail to respond correctly
- Develop hardware errors
- Refuse a supported sanitization command
- Fail verification
- Become unreliable during processing
A failed device should not simply receive a successful erasure certificate.
Instead, the organization should follow its approved exception process.
Where physical destruction is required, the asset should be documented and routed for the appropriate destruction method.
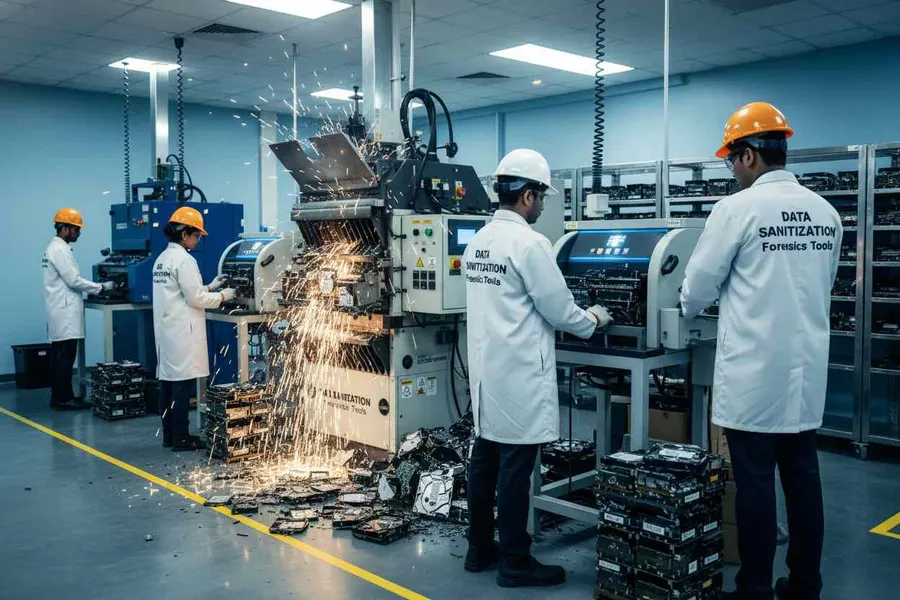
Software Compliance vs Organizational Compliance
This distinction is important.
Data Erasure Software Can Help With:
- Executing approved sanitization processes
- Supporting recognized standards
- Device identification
- Verification
- Asset-level reporting
- Certificates
- Audit records
Software Cannot Automatically Provide:
- Regulatory compliance
- Legal compliance
- An organization's privacy program
- Required policies
- Employee training
- Data retention governance
- Vendor management
- Complete chain of custody
- Independent certification
Compliance belongs to the organization's complete control environment, not to the software alone.
Compliance Framework Comparison
| Framework | Primary Concern | Data Erasure Relevance |
|---|---|---|
| DPDP Act 2023 | Personal data protection in India | Supports controlled personal-data lifecycle and applicable erasure obligations |
| GDPR | Personal data protection | Storage limitation, erasure rights and accountability |
| HIPAA | Protected health information | Secure disposal and reuse of electronic media containing ePHI |
| PCI DSS | Payment card data | Secure deletion or rendering cardholder data unrecoverable |
| R2v3 | Electronics reuse and recycling | Documented sanitization of data-bearing equipment |
Common Data Erasure Compliance Mistakes
Relying on a Factory Reset
A factory reset is not automatically equivalent to an approved media sanitization process.
Treating Formatting as Secure Erasure
Formatting changes how storage is presented to an operating system; it should not automatically be treated as proof that the underlying data is unrecoverable.
Choosing a Method Only Because It Has More Passes
Pass count alone does not determine whether a method is appropriate for modern storage.
Using an HDD Method on Every SSD
SSD and NVMe storage can require storage-aware sanitization techniques.
Keeping Only a Spreadsheet
A spreadsheet can be useful for asset management, but it should not be the only evidence of a technical sanitization operation.
Ignoring Failed Devices
A drive that fails verification should not be reported as successfully sanitized.
Assuming a Certificate Equals Compliance
A certificate documents an operation. It does not replace the organization's broader compliance obligations.
Frequently Asked Questions
Does data erasure software make an organization compliant?
No. Data erasure software can support the technical sanitization and documentation part of an organization's controls, but compliance depends on the complete set of applicable policies, procedures, safeguards and legal requirements.
Does DPDP Act require a specific data wiping method?
The DPDP Act should not be represented as prescribing one universal technical wiping algorithm. Organizations should determine appropriate technical and organizational measures based on their obligations and circumstances.
Does GDPR require a specific number of erasure passes?
No universal pass count should be presented as a GDPR requirement. The GDPR establishes broader principles and rights around personal data, including storage limitation and erasure in specified circumstances.
Does HIPAA specify one hard drive wiping method?
HIPAA requires appropriate safeguards and procedures for the final disposition of ePHI and electronic media. HHS describes clearing, purging and destruction as possible approaches depending on the circumstances.
Does PCI DSS require secure deletion?
PCI DSS requires organizations to address retention and disposal and PCI SSC states that cardholder data no longer required must be securely deleted or rendered unrecoverable.
Is NIST SP 800-88 Rev. 1 still current?
No. NIST SP 800-88 Rev. 2 was published in September 2025 and superseded Rev. 1.
Is a data erasure certificate enough for an audit?
A certificate can provide useful asset-level evidence, but whether it is sufficient depends on the organization's applicable framework, policies, auditor requirements and complete chain of controls.
What should we keep with an erased asset?
Organizations should follow their own retention policy and applicable legal, regulatory and contractual requirements. Useful records may include asset identity, sanitization method, verification result, timestamps, responsible personnel and final disposition.
What if a drive fails sanitization?
Follow the organization's documented exception process. Depending on the circumstances, the drive may require another approved sanitization attempt or physical destruction.
Build a Defensible Data Disposal Process
Secure data erasure is one part of compliance. The stronger approach is to connect the policy, the physical asset, the sanitization process, verification and the resulting evidence.
Permanent data erasure, a checked result and a certificate for every drive.