- Home
- Solutions
- Regulated Sectors
- Government Data Erasure
Data Sanitization for Government Organizations
Secure Government Data Before IT Assets Leave Your Control
Government organizations manage sensitive information across departments, agencies, offices, public-sector facilities and field locations.
When laptops, desktops, workstations, servers or storage devices are reused, redeployed, transferred, refurbished, returned or retired, the data stored on supported media should be securely erased first.
Data Sanitization Pro (DSP) provides professional government data erasure software for supported HDD, SSD and NVMe storage, with controlled erasure, verification and auditable reporting.
- Identify
- Erase
- Verify
- Certify
- Secure Data Erasure
- Offline Operation
- Verification
- Certificates
- Worldwide
Overview
Government data erasure software for secure HDD, SSD and NVMe sanitization. Verify results, generate certificates and support controlled workflows worldwide.
Why Data Sanitization Matters in Government
Government IT environments can contain information that requires careful handling throughout the complete asset lifecycle.
This may include:
- Citizen and public-service information
- Employee and administrative records
- Government documents
- Financial and procurement records
- Departmental reports
- Case and operational information
- Project documentation
- Internal communications
- Sensitive business information
The security requirement does not end when a computer or storage device is removed from active use.
A workstation may be transferred to another department.
A laptop may be reassigned to another employee.
A server may be decommissioned during an infrastructure upgrade.
A hard drive may be removed from service and sent for refurbishment or approved disposal.
A returned device may still contain information from its previous lifecycle.
Deleting files, quick formatting or reinstalling an operating system should not automatically be treated as complete media sanitization.
A professional data erasure and verification workflow helps government IT teams apply an appropriate method, verify the result and maintain documentation for the processed asset.
What Does Government Data Sanitization Mean?
Government data sanitization is the controlled process of removing stored information from supported media before an IT asset moves to its next approved lifecycle stage.
Reassignment
Erase previous information before the computer is given to another authorized user.
Redeployment
Sanitize supported storage before equipment moves between departments, offices or government facilities.
Refurbishment
Remove stored information before used equipment is prepared for another approved use.
Transfer
Sanitize data-bearing storage before an asset moves to another organizational location or approved custodian.
Return
Erase supported storage before leased or vendor-managed equipment leaves government control.
Retirement
Complete the approved logical sanitization process and retain the resulting documentation.
Data Sanitization Pro: Built for Controlled Government Data Erasure
Data Sanitization Pro combines secure data erasure, verification and reporting in one controlled software workflow.
25 Data Erasure Methods
DSP supports 25 data erasure methods for different sanitization requirements.
The selected method should be matched to the storage technology, information sensitivity and applicable government policy.
Verification
DSP provides a documented result for the completed sanitization operation.
This helps separate an attempted erasure from a process that has actually completed with a recorded verification result.
Self-Certified Data Erasure Certificates
DSP can generate self-certified, auditable data erasure certificates and reports.
The record can connect:
- Government Asset
- Device Identity
- Erasure Method
- Verification
- Result
Available information may include:
- Manufacturer
- Model
- Serial Number
- Capacity
- Interface
- Firmware
- Method
- Verification
- Timestamps
- Operator
- Asset Reference
Multi-Drive Processing
DSP supports processing up to 8 supported drives simultaneously in suitable configurations.
Offline Data Erasure
DSP supports offline sanitization workflows for controlled or restricted environments where network connectivity is limited.
USB and PXE Boot
USB and PXE boot workflows can support suitable system-drive sanitization and larger government endpoint deployments.
From Government Asset Detection to a Verified Erasure Certificate
- 01
Identify
Connect the supported storage device and capture the available device information.
- Manufacturer
- Model
- Serial Number
- Capacity
- Interface
- Firmware
- 02
Assess
Review the storage technology and determine the appropriate supported sanitization method.
- 03
Erase
Run the selected secure data erasure process.
- 04
Verify
Verify the completed operation and record the result.
- 05
Certify
Generate the corresponding data erasure certificate or report.
This creates a device-level record that can be associated with the government asset and its processing history.
Government Laptop and Desktop Data Erasure
Government departments often manage large numbers of laptops and desktops.
Equipment can be replaced because of:
- Employee transfers
- Department restructuring
- Technology refresh
- Office relocation
- Hardware upgrades
- Lease expiry
- Refurbishment
- Resale
- Retirement
Before a computer is reassigned or removed from government control, the supported storage should be processed through the appropriate sanitization workflow.
DSP supports secure data erasure workflows for supported HDD, SSD and NVMe storage.
A running Windows system normally cannot erase the physical drive from which it is currently operating.
For suitable deployments, DSP supports USB and PXE boot workflows so the system can start in the sanitization environment before its target storage is processed.
Government HDD Data Erasure
Hard disk drives can contain information long after they have been removed from active service.
Professional HDD data erasure software can help government organizations securely process supported drives before:
- Reuse
- Redeployment
- Refurbishment
- Transfer
- Retirement
DSP provides a structured workflow:
- Detect
- Select Method
- Erase
- Verify
- Certify
The physical HDD remains intact because DSP performs software-based logical data destruction rather than physical shredding.
Government SSD Data Erasure
Modern government computers increasingly use solid-state storage.
SSD sanitization requires an appropriate approach because SSDs use NAND flash and controller-managed storage technologies.
DSP supports supported SSD data erasure workflows based on the capabilities of the actual drive.
Depending on the device, supported operations may include:
- Secure Erase
- Sanitize functions
- Cryptographic Erase
- Other supported sanitization methods
The actual operation should be selected according to the SSD, controller, firmware, interface path and government security requirements.
Government NVMe Data Erasure
NVMe storage is increasingly used in modern laptops, desktops and workstations.
NVMe communicates through the PCIe interface and may expose device-level sanitization capabilities depending on the specific implementation.
DSP supports NVMe data erasure workflows for supported devices.
The process should follow:
- Identify
- Assess Capability
- Select
- Erase
- Verify
- Certify
The exact sanitization operation depends on the NVMe controller, firmware, connection path and available capabilities.
Data Sanitization for Government Departments
Government organizations may have multiple departments using separate IT environments.
Examples include:
- Finance
- Administration
- Education
- Healthcare
- Transport
- Municipal Services
- Public Works
- Revenue
- Regulatory Offices
Computers and storage may move between these departments during their lifecycle.
A standardized government data wiping process helps IT teams address stored information before an asset is reassigned, transferred, refurbished or retired.
Government Agency Data Erasure
Government agencies may operate distributed offices and field locations.
Devices can move through:
- Agency Office
- Field Location
- Central IT
- Reassignment
- Retirement
Each stage can introduce another lifecycle transition.
Professional data erasure software can help standardize the storage sanitization stage for supported devices.
DSP provides:
- Secure Erasure
- Verification
- Certificate
for completed supported workflows.
Public Sector Data Sanitization
Public-sector organizations often manage large technology estates.
These can include:
- Employee computers
- Administrative workstations
- Laptops
- Servers
- Storage devices
- Backup media
- Retired IT equipment
During modernization projects, equipment may be reused internally or transferred to another approved lifecycle.
A controlled public sector data erasure workflow can help protect information while creating documentation for processed storage devices.
Government Server and Storage Data Erasure
Government organizations may operate local servers, storage systems and data-centre infrastructure.
When physical storage devices are removed during an infrastructure upgrade or decommissioning project, supported drives may require secure sanitization before they move to their next approved stage.
DSP can support server storage data erasure for compatible physical media.
For live servers, shared storage, virtual environments and specialized infrastructure, the sanitization workflow should be planned around the actual architecture before data-bearing storage is processed.
Government Data Erasure for Restricted Environments
Some government facilities operate restricted, isolated or controlled IT environments.
DSP supports offline data sanitization workflows for suitable deployments where internet connectivity is restricted.
A controlled offline workflow can include:
- Local Device Detection
- Local Erasure
- Local Verification
- Local Certificate Generation
This can help organizations keep supported data-bearing assets within their designated processing environment.
Offline and Air-Gapped Government Data Erasure
Where network connectivity is unavailable or intentionally restricted, an online-only sanitization workflow may not be practical.
DSP supports offline operation for suitable deployments, allowing the core sanitization workflow to run without depending on an active internet connection.
This can be useful for:
- Restricted government facilities
- Secure IT rooms
- Isolated processing areas
- Controlled asset staging locations
- Air-gapped environments
USB Boot Data Erasure for Government Computers
A running operating system normally cannot erase the physical system drive from which it is operating.
For suitable deployments, DSP supports USB boot workflows so a supported computer can start into the sanitization environment before its system storage is processed.
This can be useful during:
- Government laptop refresh
- Desktop retirement
- Workstation replacement
- Department transfers
- IT asset disposition
PXE Data Erasure for Government Fleets
Government departments with large endpoint fleets may need a repeatable deployment model.
DSP supports PXE deployment for up to 64 computers by default, with configured capacity adjustable for larger environments.
Supported systems can boot into the sanitization environment and process their available storage.
Actual throughput depends on:
- Network Capacity
- Hardware Configuration
- Storage Interfaces
- Processing Resources
Government Data Erasure Verification
For government asset retirement, simply marking an asset as "wiped" does not provide the same detail as a device-level processing record.
DSP separates the erasure process from its verification result.
The workflow becomes:
- Erase
- Verify
- Record
This helps government IT teams maintain a clearer record of the completed sanitization operation.
A failed or incomplete operation should not be reported as a successful sanitization result.
Government Data Erasure Certificates and Audit Records
A certificate should be linked to the actual storage asset that was processed.
DSP can generate self-certified, auditable data erasure certificates and reports.
A record may associate:
- Asset Number
- Serial Number
- Erasure Method
- Verification Result
- Certificate
Available information can include:
- Manufacturer
- Model
- Serial number
- Capacity
- Interface
- Firmware
- Erasure method
- Verification status
- Processing timestamps
- Operator information
- Asset reference
This creates a structured government data erasure audit trail.
Government Asset Reconciliation
Large government IT refresh projects may involve many assets.
A structured sanitization record can help teams connect:
- Inventory
- Device
- Erasure Job
- Verification
- Certificate
This is useful when asset records need to remain associated with individual storage devices throughout the lifecycle.
The software-generated certificate documents the sanitization job performed on the specific asset.
Government Data Erasure Before Reuse and Redeployment
Government hardware does not always need to be physically destroyed.
Where policy allows continued use, suitable assets can move through another lifecycle stage after successful sanitization.
Reuse
Erase previous information before assigning the device to another authorized user.
Redeployment
Sanitize before moving equipment between departments or facilities.
Refurbishment
Erase stored information before preparing used equipment for another approved role.
Transfer
Complete the required sanitization before the asset changes organizational control.
Retirement
Complete the approved sanitization process and retain the resulting documentation.
Government IT Asset Disposition and Data Erasure
IT Asset Disposition (ITAD) is an important part of government technology lifecycle management.
A typical workflow can be:
- Inventory
- Data Sanitization
- Verification
- Documentation
- Approved Disposition
Data Sanitization Pro can support the data erasure stage for compatible storage devices.
Where a device cannot be reliably sanitized, the organization's approved alternative media-disposition process should be followed.
Government Data Erasure for Agencies and Contractors
Government agencies may work with authorized contractors, service providers and technology partners.
Equipment can move through:
- Government Organization
- Authorized Service Provider
- Repair / Upgrade
- Government Organization
When a data-bearing device enters an approved sanitization workflow, the storage can be securely processed and documented according to the applicable organizational requirements.
DSP can support the erasure, verification and reporting stages for compatible storage.
Multi-Drive Data Erasure for Government
Government IT departments may need to process multiple devices during a hardware refresh or asset retirement project.
DSP supports up to 8 supported drives simultaneously in suitable configurations.
This can be useful for:
- Government laptop refresh
- Desktop replacement
- HDD retirement
- SSD retirement
- NVMe sanitization
- Server storage upgrades
- Refurbishment
- ITAD processing
Actual processing capacity depends on the hardware configuration, storage controllers, interfaces and system resources.
Worldwide Government Data Erasure
Data protection and secure media disposal are important across government organizations worldwide.
Data Sanitization Pro can support government organizations, public-sector bodies, agencies, regulatory institutions and government contractors worldwide, subject to deployment requirements, licensing, project scope and applicable service availability.
Government Ministries Worldwide
Sanitize supported storage during equipment replacement and retirement.
Government Departments Worldwide
Process computers and storage before reassignment or approved disposition.
Public-Sector Organizations Worldwide
Standardize suitable data erasure workflows across distributed IT assets.
Regulatory Bodies Worldwide
Maintain controlled sanitization and documentation workflows for supported devices.
Government Contractors Worldwide
Process supported storage according to applicable contractual and organizational requirements.
Local and Municipal Authorities Worldwide
Secure retired computers and storage before reuse, transfer or disposal.
Government Data Sanitization Standards
Data sanitization should follow the standard or approved process applicable to the organization, media and information sensitivity.
NIST SP 800-88 Rev. 2
NIST SP 800-88 Rev. 2 is the current NIST publication for media sanitization. It was published on September 26, 2025, superseding Rev. 1, and emphasizes establishing a media-sanitization program and selecting appropriate techniques and controls based on the media and information involved.
IEEE 2883
IEEE 2883 provides technology-focused requirements and guidance related to storage sanitization.
Organizational and Government Policies
Government organizations may also have internal policies, procurement requirements, contractual controls or national standards governing media sanitization and disposal.
The important principle is:
Storage Technology + Information Sensitivity + Government Policy + Intended Disposition
should all be considered when selecting the sanitization approach.
A software-generated certificate documents the completed sanitization job. It should not by itself be presented as proof that the organization automatically satisfies every legal, regulatory, contractual or government-security requirement.
Government Data Sanitization Before Hardware Release
Before equipment is released for its next lifecycle stage, organizations can use a controlled workflow:
- Identify
- Sanitize
- Verify
- Certify
- Release
This can apply to supported devices moving toward:
- Reuse
- Redeployment
- Refurbishment
- Resale
- Return
- Retirement
The final decision should follow the government's asset and information-security policy.
When Government Storage Cannot Be Reliably Erased
Software-based sanitization depends on the storage device being accessible and exposing the required functionality.
Additional assessment may be required when a device:
- Is not detected
- Has a controller problem
- Has firmware limitations
- Cannot complete the selected operation
- Does not expose the required sanitization functionality
- Is connected through an unsupported bridge or adapter
- Cannot provide the required verification result
A failed or incomplete process should not be treated as a successful sanitization result.
Data Sanitization Pro is a software-based logical data destruction solution. It does not physically shred, crush or drill storage devices.
Where software erasure cannot reliably meet the required outcome, the government organization's approved alternative media-disposition process should be followed.
Government Storage Health Assessment Before Reuse
Data sanitization and hardware condition are separate decisions.
A drive can complete its sanitization successfully and still require a technical assessment before reuse.
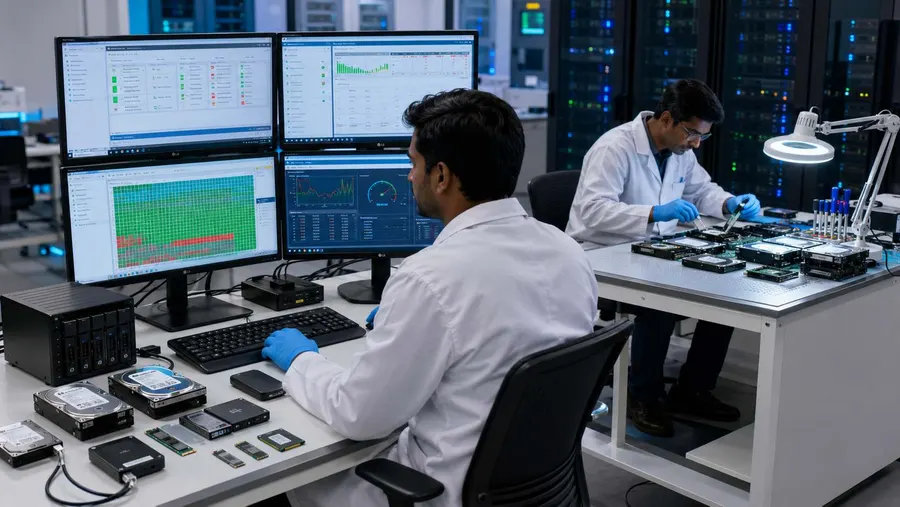
Available device information may help teams review:
- Drive Health
- SMART Information
- Error Conditions
- Storage Status
- Device Information
This separates two questions:
Sanitization Result: Was the data erasure completed and verified?
Asset Condition: Is the device suitable for its next lifecycle stage?
Who Uses Government Data Erasure Software?
Government Ministries
For secure IT asset lifecycle management.
Government Departments
For computer reassignment, refresh and retirement.
Government Agencies
For controlled storage sanitization and documentation.
Public-Sector Organizations
For structured IT asset retirement and reuse workflows.
Regulatory Bodies
For secure handling of supported data-bearing storage.
Local and Municipal Authorities
For computer and storage lifecycle management.
Law Enforcement Organizations
For controlled sanitization of supported IT storage according to applicable policies.
Government Contractors
For secure data erasure workflows where required by organizational or contractual requirements.
Why Choose Data Sanitization Pro for Government?
Secure Data Erasure Software
Controlled software-based logical data destruction for supported storage.
25 Erasure Methods
Multiple supported sanitization methodologies for different requirements.
Verification
Record the result of the completed sanitization operation.
Self-Certified Certificates
Generate auditable data erasure certificates and reports.
Up to 8 Drives
Process multiple supported drives simultaneously in suitable configurations.
Offline Operation
Support controlled environments where internet access is restricted.
USB and PXE Boot
Support suitable system-drive and fleet sanitization workflows.
Device-Level Reporting
Connect each processed asset with its identity, selected method and verification result.
Asset Lifecycle Support
Secure supported storage before reuse, redeployment, refurbishment, transfer, return or retirement.
Worldwide Government Support
Support suitable government and public-sector deployments worldwide, subject to licensing, project scope and deployment requirements.
Frequently Asked Questions
What is government data sanitization?
Government data sanitization is the controlled removal of stored information from supported storage devices before government IT assets are reused, redeployed, transferred, refurbished, returned or retired.
What is government data erasure software?
Government data erasure software is used to securely process supported storage devices, verify the result and generate documentation associated with the processed asset.
Why is data sanitization important for government organizations?
Government devices can contain administrative, citizen, financial, operational and other sensitive information. Secure media sanitization helps address stored data before an asset changes lifecycle stage.
Is deleting files enough before a government computer is reused?
Deleting files or formatting a storage device should not automatically be treated as complete media sanitization. An appropriate professional sanitization process should be selected according to the media and organizational requirements.
Can Data Sanitization Pro erase government HDDs and SSDs?
Yes. DSP supports supported HDD, SSD and NVMe sanitization workflows according to the capabilities of the actual storage devices.
Does DSP support NIST SP 800-88 Rev. 2?
DSP supports sanitization workflows that can be aligned with applicable NIST-based organizational processes. The actual method should be matched to the storage media and the government's applicable policy. NIST SP 800-88 Rev. 2 is the current NIST media-sanitization publication.
Can government organizations use DSP offline?
Yes. DSP supports offline data sanitization workflows for suitable controlled environments.
Can DSP work in air-gapped environments?
DSP supports offline operation for suitable deployments. Whether a specific air-gapped environment is compatible depends on the deployment configuration and operational requirements.
Can government agencies erase system drives?
A running Windows installation normally cannot erase the physical drive it is currently using. For suitable deployments, DSP supports USB and PXE boot workflows for system-drive sanitization.
How many drives can DSP process simultaneously?
DSP supports up to 8 supported drives simultaneously in suitable configurations.
Does DSP generate government data erasure certificates?
DSP can generate self-certified, auditable data erasure certificates and reports containing relevant device, process and verification information.
Is Data Sanitization Pro a physical destruction tool?
No. DSP is a software-based logical data destruction solution. It does not physically shred, crush or drill storage devices.
Can government organizations use DSP worldwide?
Yes. DSP can support suitable government and public-sector deployments worldwide, subject to licensing, deployment requirements, project scope and service availability.
Can a failed drive be certified as successfully erased?
No. A failed or incomplete sanitization operation should not be treated as a successful result.
Related Solutions
Defence
Offline erasure with verification and certificates
Read MoreBanking & Finance
Secure financial data before assets change hands
Read MoreInsurance
For insurers, brokers and TPAs retiring IT assets
Read MoreHealthcare
Secure patient data before devices move on
Read MoreEducation & Research
For schools, colleges, universities and research centres
Read MoreSecure Government Data Before the Next Lifecycle Stage
Before supported computers and storage devices are reused, redeployed, transferred, refurbished, returned or retired, use a controlled and verifiable data erasure process.